🚀 End-to-End DevOps Project: Deploying Swiggy Clone with Terraform, Jenkins, SonarQube, Trivy & Docker


In this production-ready DevOps implementation guide, we build a complete automated CI/CD and DevSecOps pipeline from scratch. Starting from Infrastructure as Code (IaC) using Terraform on AWS, we set up and configure Jenkins, integrate SonarQube for continuous code quality analysis, enforce Quality Gates, run Trivy vulnerability scans on filesystem and container images, and automate containerized deployment of a Swiggy Clone web application 🍔☕.
Watch the complete, end-to-end video tutorial explaining every step of this project:
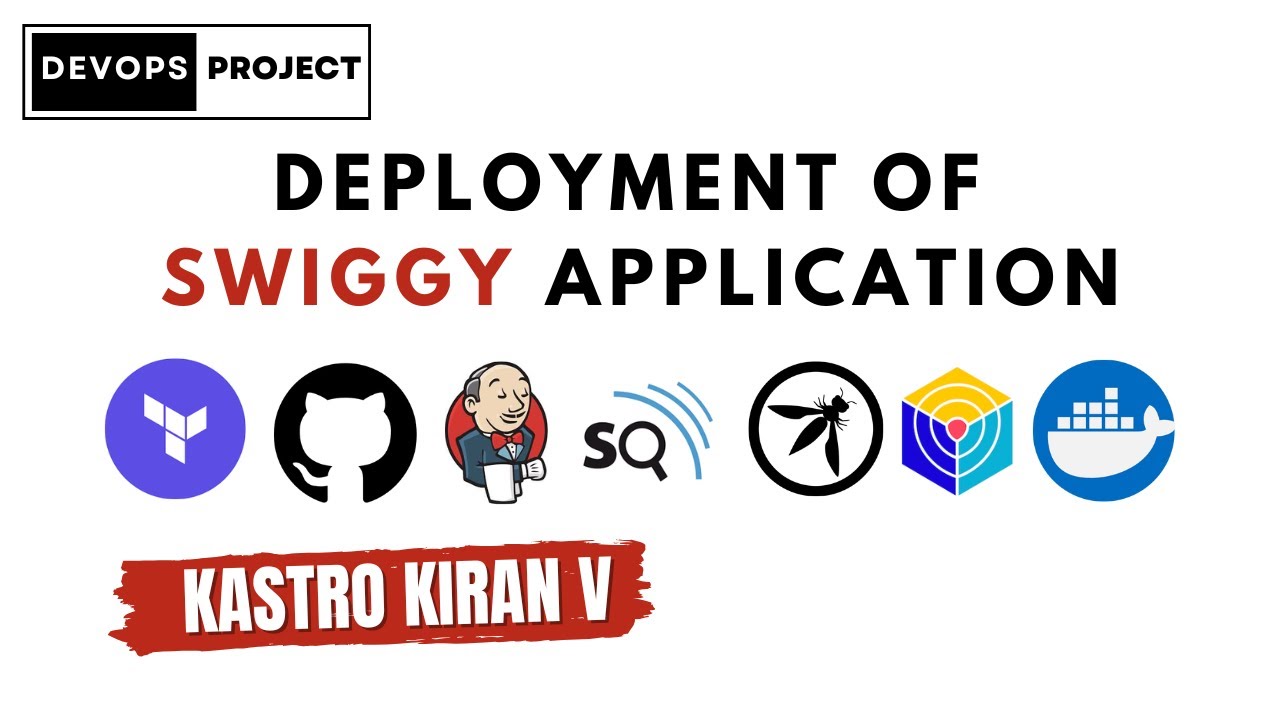
📺 Watch Full Video: DevOps Real-time Project | Deployment of SWIGGY App (YouTube)
Author: Kastro Kiran V
[ Git / GitHub ] ───► [ Jenkins CI Server ]
                             │
                             ├─► 1. Clean Workspace & Git Checkout
                             ├─► 2. SonarQube Static Analysis & Quality Gate Check
                             ├─► 3. NPM Dependencies Installation
                             ├─► 4. Trivy Filesystem Vulnerability Scan
                             ├─► 5. Docker Image Build & Tagging
                             ├─► 6. Trivy Container Image Security Scan
                             ├─► 7. Push to DockerHub Registry
                             └─► 8. Deploy Container (Docker Run on Port 3000) ──► [ Live Users ]
Ensure your AWS EC2 instance has appropriate resources (Recommended: t2.large or t3.large, 2–4 vCPUs, 8 GB RAM, 30 GB EBS Storage) and the following inbound ports opened in your Security Group:
| Service | Port | Protocol | Purpose |
|---|---|---|---|
| SSH | 22 |
TCP | Remote EC2 Administration |
| Jenkins | 8080 |
TCP | Jenkins CI/CD Automation Web UI |
| SonarQube | 9000 |
TCP | SonarQube Code Quality Dashboard |
| Swiggy App | 3000 |
TCP | Live Deployed React/Node Application |
We use Terraform to define our cloud infrastructure declaratively, ensuring repeatable and reproducible deployments.
🔗 GitHub Repository for Terraform Code:
👉 Terraform-Script-Swiggy-sandeep
main.tf→ Terraform backend configuration, provider pinning, and core infrastructure setup.provider.tf→ AWS provider definition, specifying target region and credentials.resource.tf→ Provisions EC2 instance, VPC, Subnets, Security Groups, IAM Roles, and Key Pairs.variables.tf/outputs.tf→ Dynamic input variables (AMI, instance types) and useful outputs (public IP address, DNS).
# 1. Initialize provider plugins and backend
terraform init

# 2. Review execution plan and dry-run infrastructure diff
terraform plan

# 3. Provision EC2 instance, networking, and security groups
terraform apply -auto-approve

# (When finished with project) Teardown all cloud resources to avoid costs
# terraform destroy -auto-approve
🎉 Your EC2 instance and networking stack are now provisioned and running!
You can connect directly from your browser using AWS EC2 Instance Connect:
- Navigate to AWS Management Console → EC2 → Instances.
- Select your provisioned instance.
- Click Connect → EC2 Instance Connect → Connect.

Once your setup script/userdata has finished running, access the web dashboards:
- Jenkins Web UI:
http://<EC2-PUBLIC-IP>:8080

- SonarQube Dashboard:
http://<EC2-PUBLIC-IP>:9000

Navigate to Manage Jenkins → Plugins → Available Plugins, search for and install:
- ✅ Eclipse Temurin installer (JDK): Provides Java runtimes required by Jenkins and the SonarQube Scanner.
- ✅ Pipeline Stage View: Visualizes pipeline stages cleanly in real-time.
- ✅ SonarQube Scanner: Enables static code analysis and transmits findings directly to the SonarQube dashboard.
- ✅ NodeJS: Allows Jenkins to manage and switch Node.js versions for front-end dependency builds.
- ✅ Docker (Common, Pipeline, API): Grants pipeline access to Docker commands for building, tagging, and pushing images.

Once plugins are installed, configure runtime versions under Manage Jenkins → Tools (Global Tool Configuration):
- JDK Installation:
- Name:
jdk17 - Source: Install automatically from adoptium.net (Java 17 LTS).
- Name:
- SonarQube Scanner Installations:
- Name:
sonar-scanner - Version:
sonar-scanner (v6.2.1.4610)or latest stable.
- Name:
- NodeJS Installations:
- Name:
node20 - Version:
NodeJS 20.x(LTS).
- Name:
- Docker Installations:
- Name:
docker - Version: Latest Docker CLI.
- Name:

💾 Click Apply and Save.
- Access SonarQube at
http://<EC2-IP>:9000(Default credentials:admin/admin). - Go to Administration → Security → Users.
- Under the Tokens column for
Administrator, click the token icon. - Name the token
sonar-tokenand click Generate. - Copy the generated token string.

- Go to Manage Jenkins → Credentials → System → Global credentials → Add Credentials.
- Kind:
Secret text - Secret: Paste the generated SonarQube token.
- ID:
sonar-token - Description:
SonarQube Authentication Token - Click Create.

To allow SonarQube to notify Jenkins when Quality Gate checks pass or fail:
- In SonarQube, navigate to Administration → Configuration → Webhooks.
- Click Create.
- Name:
jenkins-webhook - URL:
http://<EC2-PUBLIC-IP>:8080/sonarqube-webhook/ - Click Create.

- Go to Manage Jenkins → System (Configure System).
- Scroll to the SonarQube servers section.
- Check Enable injection of SonarQube server configuration as environment variables.
- Click Add SonarQube:
- Name:
sonar-server(must match the name used in your Jenkinsfile) - Server URL:
http://<EC2-PUBLIC-IP>:9000 - Server authentication token: Select
sonar-tokenfrom the dropdown.
- Name:
- Click Save.

To enable Jenkins to authenticate and push the built Docker image to DockerHub:
- Go to Manage Jenkins → Credentials → System → Global credentials → Add Credentials.
- Fill in the fields:
- Kind:
Username with password - Username: Your DockerHub username
- Password: Your DockerHub password or Personal Access Token
- ID:
docker-creds(referenced in pipeline script) - Description:
DockerHub Registry Credentials
- Kind:

- Click Create to save the credentials.

💡 Tip: Ensure the
jenkinssystem user has permissions to interact with the Docker daemon on the EC2 host:sudo usermod -aG docker jenkins sudo systemctl restart jenkins
🔗 GitHub Repository for Application Code:
👉 DevOps-Project-Swiggy
- Go to Jenkins Dashboard → New Item.
- Enter item name:
Swiggy-DevOps-Pipeline. - Select Pipeline and click OK.

- Scroll down to the Pipeline script definition block and paste the declarative
Jenkinsfile:
pipeline {
    agent any

    tools {
        jdk 'jdk17'
        nodejs 'node20'   // Node.js 20 LTS
    }

    environment {
        SCANNER_HOME = tool 'sonar-scanner'
        DOCKER_IMAGE = 'sandeepallakonda/swiggy'
        DOCKER_TAG   = 'latest'
    }

    stages {
        stage('Clean Workspace') {
            steps {
                cleanWs()
            }
        }

        stage('Checkout from Git') {
            steps {
                git branch: 'master',
                    url: 'https://github.com/NotHarshhaa/DevOps-Projects/tree/master/DevOps-Project-41/DevOps-Project-Swiggy'
            }
        }

        stage('SonarQube Code Analysis') {
            steps {
                withSonarQubeEnv('sonar-server') {
                    sh """
                        $SCANNER_HOME/bin/sonar-scanner \
                          -Dsonar.projectKey=Swiggy \
                          -Dsonar.projectName=Swiggy \
                          -Dsonar.sources=.
                    """
                }
            }
        }

        stage('Quality Gate') {
            steps {
                script {
                    timeout(time: 2, unit: 'MINUTES') {
                        waitForQualityGate abortPipeline: true
                    }
                }
            }
        }

        stage('Install Dependencies') {
            steps {
                sh "npm install"
            }
        }

        stage('Trivy Filesystem Security Scan') {
            steps {
                sh "trivy fs . --exit-code 0 --severity HIGH,CRITICAL -f table -o trivy-fs-report.txt"
                archiveArtifacts artifacts: 'trivy-fs-report.txt', allowEmptyArchive: true
            }
        }

        stage('Docker Build & Push') {
            steps {
                script {
                    withDockerRegistry(credentialsId: 'docker-creds', toolName: 'docker') {
                        sh """
                            docker build -t ${DOCKER_IMAGE}:${DOCKER_TAG} .
                            docker push ${DOCKER_IMAGE}:${DOCKER_TAG}
                        """
                    }
                }
            }
        }

        stage('Trivy Image Vulnerability Scan') {
            steps {
                sh "trivy image ${DOCKER_IMAGE}:${DOCKER_TAG} --exit-code 0 --severity HIGH,CRITICAL -f table -o trivy-image-report.txt"
                archiveArtifacts artifacts: 'trivy-image-report.txt', allowEmptyArchive: true
            }
        }

        stage('Deploy to Container') {
            steps {
                sh """
                    docker rm -f swiggy || true
                    docker run -d --name swiggy -p 3000:3000 ${DOCKER_IMAGE}:${DOCKER_TAG}
                """
            }
        }
    }

    post {
        always {
            echo "Pipeline execution finished."
        }
        success {
            echo "🎉 Swiggy Application deployed successfully to production container!"
        }
        failure {
            echo "❌ Pipeline failed! Please review stage logs and security reports."
        }
    }
}Click Build Now on the Jenkins pipeline page.
- Clean Workspace → Prepares fresh workspace directory.
- Checkout from Git → Clones source code from GitHub repository.
- SonarQube Analysis → Performs SAST code scanning and transmits metric data.
- Quality Gate → Verifies SonarQube Quality Gate threshold status.
- Install Dependencies → Installs NPM packages via Node 20.
- Trivy FS Scan → Audits repository source dependencies for HIGH/CRITICAL CVEs.
- Docker Build & Push → Builds production container image and pushes to DockerHub.
- Trivy Image Scan → Scans the compiled container image layers for known vulnerabilities.
- Deploy Container → Launches container exposed on port 3000.

Open your web browser and navigate to:
👉 http://<EC2-PUBLIC-IP>:3000

🍔 The Swiggy Clone web application is now successfully running live in Docker!
By completing this project, you have implemented a real-world enterprise DevSecOps workflow:
- ☁️ Infrastructure as Code (IaC): Automated cloud resource provisioning with Terraform.
- 🔄 Continuous Integration (CI): Automated builds, linting, and dependency tracking with Jenkins.
- 🛡️ DevSecOps & Code Quality: SonarQube static code analysis + Quality Gate enforcement.
- 🔒 Vulnerability Management: Trivy multi-stage scanning on filesystems and container layers.
- 📦 Containerization & CD: Automated image packaging and production deployment with Docker.
This project is crafted by Harshhaa 💡.
I’d love to hear your feedback! Feel free to share your thoughts.